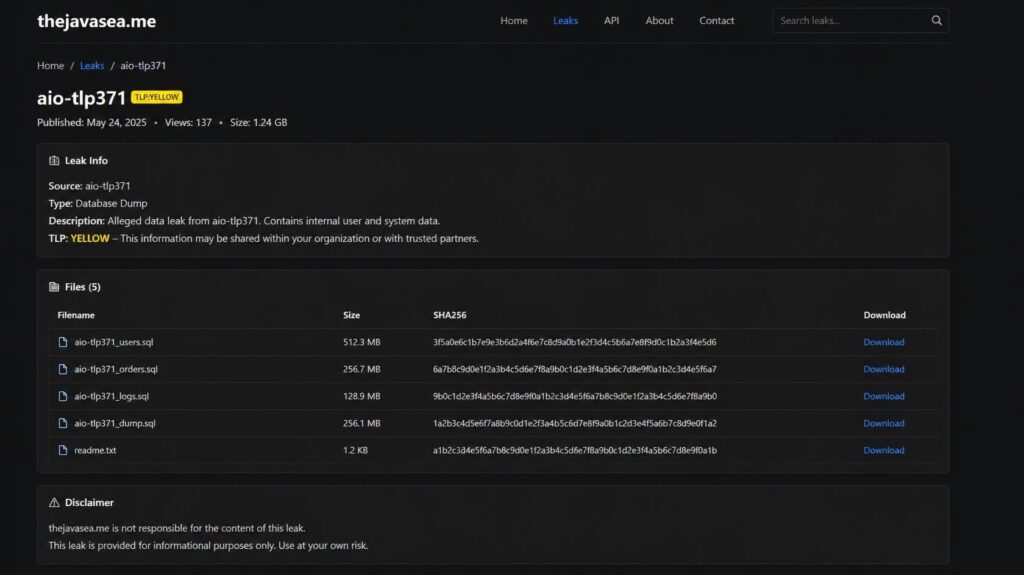
The phrase thejavasea.me leaks aio-tlp371 has appeared in online searches and articles discussing alleged leaked digital content. If you have come across this term, you may be wondering what AIO-TLP371 means, whether the reported material is authentic, and whether your personal information could be at risk.
The most important point is that online discussion does not automatically prove a security breach. Available public information does not independently establish the exact contents, origin, authenticity, or scope of the material associated with this label. Some websites describe it as a collection or archive, but those descriptions should not be treated as verified facts without reliable supporting evidence.
Expand Magazine
+1
This guide explains the term, separates reported claims from confirmed information, and explores the cybersecurity and privacy risks associated with unknown leak archives. You will also learn how to protect your accounts, check for possible data exposure, and respond if you believe your information has been compromised.
What Is TheJavaSea.me Leaks AIO-TLP371?
The phrase combines the domain name TheJavaSea.me, the word “leaks,” and the identifier AIO-TLP371. Online articles use this combination when discussing an alleged digital archive or collection of files. Some describe AIO as meaning “all-in-one,” a common abbreviation for a bundle that brings multiple items together. However, the label alone does not reveal what the collection contains or where the material originated.
expandmagazine.co.uk
+1
It is also important to separate a website’s reputation from evidence about a specific incident. A website may be mentioned in discussions about leaked material without independently proving that the material is genuine, recently obtained, or connected to a particular victim. A reliable assessment requires more than a search result or an article repeating another website’s claims.
For readers in the United States, the practical concern is whether the alleged material involves personal information, copyrighted files, private communications, or other sensitive content. Each possibility raises different privacy, security, and legal issues. Until credible evidence establishes the details, it is more accurate to describe AIO-TLP371 as an unverified leak-related label than to present it as a confirmed data breach.
What Does AIO-TLP371 Mean?
The name AIO-TLP371 looks technical, but its exact meaning in this context has not been independently established. Understanding the parts of the label can help explain why some online descriptions may be misleading.
AIO: The Common Meaning
AIO commonly stands for “all-in-one.” In technology, it can describe a combined product, a software package, or a collection of resources gathered under one label. In discussions about alleged leaks, websites may use the same abbreviation to describe a bundle of files.
However, this general meaning does not confirm that the specific AIO-TLP371 collection contains information from multiple breaches. Nor does it prove that every item in a purported archive is authentic, complete, or related to the same incident.
TLP371: An Unverified Identifier
The meaning of “TLP371” is less clear. It may function as a label used in online discussions, but there is no reliable evidence establishing what the number represents in this particular case.
One important distinction concerns the official Traffic Light Protocol, a cybersecurity information-sharing standard maintained by the Forum of Incident Response and Security Teams (FIRST). The current standard recognizes four main labels: TLP:RED, TLP:AMBER, TLP:GREEN, and TLP:CLEAR. TLP371 is not one of those official designations.
first.org
+1
Therefore, it would be misleading to claim that AIO-TLP371 has an official security classification simply because its name contains the letters TLP. Without documentation from a credible source, its precise meaning remains uncertain.
Is TheJavaSea.me AIO-TLP371 a Confirmed Data Breach?
A key question is whether AIO-TLP371 represents a verified cybersecurity incident. Based on the public sources reviewed for this article, the exact origin, contents, affected parties, and scope of the alleged collection have not been independently established. Several online articles discuss the label, but repetition across websites is not the same as independent confirmation.
What Is Actually Known
+1
A confirmed data breach usually has supporting evidence. Depending on the circumstances, that may include a notice from an affected organization, a statement from a regulator, an investigation by a recognized security researcher, or a credible incident report. A trustworthy report should identify what is known, explain how it was verified, and clearly acknowledge any gaps.
Here is how to interpret the available information:
| Claim | Responsible assessment |
| The phrase AIO-TLP371 appears online | Confirmed by indexed search results |
| AIO means “all-in-one” | Common interpretation, not proof of this archive’s contents |
| TLP371 is an official FIRST classification | Incorrect |
| The archive’s contents are fully verified | Not established |
| A specific company is confirmed as the victim | Not established |
| A verified number of affected people is available | Not established |
| The label proves a new cyberattack occurred | No |
These distinctions matter because exaggerated breach claims can cause unnecessary alarm. At the same time, uncertainty should not lead people to ignore basic digital security. You can protect your accounts without accessing the alleged files or assuming that a breach has definitely occurred.
What Are the Risks of Alleged Leak Archives?
Even when the details of a particular archive remain uncertain, interacting with unknown files and untrusted download sites can create real risks. The safest approach is to avoid downloading or opening alleged leaked material simply to discover what it contains.
Malware and Malicious Downloads
Files advertised as leaked databases, archives, or software bundles may be used to distribute malicious programs. A download might contain an executable disguised as a document, a password-protected archive, or a file that attempts to exploit an outdated application.
Malware can steal saved passwords, monitor activity, collect browser information, or provide unauthorized access to a device. A file’s name, icon, or claimed size does not establish that it is safe.
Avoid installing unknown programs or running scripts supplied by an untrusted website. Keep your operating system, browser, and security software updated, and do not disable security protections to open a suspicious file.
Stolen Credentials and Account Takeover
If an actual dataset contains exposed usernames, email addresses, or passwords, criminals may use that information to attempt account takeovers. One common technique is credential stuffing, in which attackers try a password exposed in one incident on other services.
This risk is especially serious when people reuse passwords across email, banking, shopping, and social media accounts. A password stolen from a low-profile service might also unlock a more important account.
Use a different password for every account. A password manager can help you create and store strong, unique credentials without having to memorize them all.
Phishing and Social Engineering
An alleged leak can also become a theme for phishing campaigns. Scammers may send messages claiming that your information appears in AIO-TLP371 and ask you to click a link, verify your identity, or pay a fee to remove your details.
These messages can look convincing, especially if they include your name or email address. However, knowing a few personal details does not prove that a sender has access to a genuine new breach.
Do not open unexpected links or attachments. Instead, visit the relevant service through its official website or app and check for legitimate security notifications.
Privacy and Reputational Harm
Some alleged archives may be described as containing private conversations, personal documents, images, or other sensitive information. The actual contents of AIO-TLP371 have not been independently established, so such claims should not be repeated as facts.
Nevertheless, unauthorized sharing of private material can cause serious harm. It may expose individuals to harassment, impersonation, fraud, or unwanted public attention.
Do not repost, forward, or publish private files to investigate their authenticity. If you encounter material that appears to expose someone’s personal information, report it through an appropriate platform or official channel instead.
How to Protect Your Personal Information
You do not need to visit TheJavaSea.me or download AIO-TLP371 to improve your online security. A few practical steps can reduce the chance that an exposed password or a deceptive message will lead to further problems.
1. Change Reused or Exposed Passwords
Start with your primary email account because it often controls password resets for other services. If you have evidence that a password was exposed, change it on every account where you used it.
Create a unique password for each service. Avoid small variations of the same password, such as adding a different number to the end. A password manager can generate and store stronger alternatives.
If you suspect someone has accessed an account, sign out unfamiliar sessions, review account recovery details, and check for changes you did not make.
2. Enable Multifactor Authentication
Multifactor authentication (MFA) adds another verification step beyond your password. Depending on the service, that step might involve an authenticator app, a security key, or a confirmation prompt.
This extra layer makes it harder for someone to access your account with a stolen password alone. The U.S. Cybersecurity and Infrastructure Security Agency explains that MFA improves account security because an attacker generally needs to compromise more than one authentication factor.
CISA
Enable MFA on your email, financial accounts, social media profiles, and any service that stores sensitive information. Where available, consider passkeys or phishing-resistant security keys.
3. Check Your Email Address Safely
A reputable breach-notification service can help you determine whether an email address appears in a known data breach. For example, you can use Have I Been Pwned at haveibeenpwned.com.
Use the service’s official website rather than a link from an unfamiliar message. A result can indicate that your address appeared in a known incident, but it does not necessarily prove that your information is part of AIO-TLP371.
Likewise, a result showing no known exposure does not guarantee that your information has never been compromised. Not every incident is reported, verified, or included in every monitoring service.
4. Review Financial and Online Accounts
If you suspect that financial details or identity information have been exposed, review recent account activity for transactions or changes you do not recognize.
For U.S. readers, the Federal Trade Commission’s IdentityTheft.gov provides guidance for people dealing with suspected identity theft. If a bank or payment service may be affected, contact it through its official phone number or website.
Watch for unexpected password-reset emails, unfamiliar login alerts, new account notifications, and messages about transactions you did not make. Act on specific warning signs rather than assuming every unusual message is evidence of this particular alleged leak.
How Can You Verify Claims About AIO-TLP371?
A reliable investigation begins with source quality, not with the number of websites repeating the same phrase. When evaluating claims about thejavasea.me leaks aio-tlp371, look for evidence that can be checked independently.
Look for Primary Sources
A primary source provides information directly from the organization or authority involved. Depending on the claim, useful sources may include:
- An official security notice from an affected organization.
- A statement from a relevant regulator or law enforcement agency.
- A technical report from a recognized cybersecurity research team.
- A documented incident analysis that explains the evidence and limitations.
- A notification from a trusted breach-monitoring service.
A website that merely describes an alleged archive is not necessarily a primary source. If several articles use the same wording but cite no original evidence, they may all rely on the same unverified claim.
Check Dates and Supporting Evidence
Publication dates can be misleading. An article posted in 2026 does not prove that the alleged incident happened in 2026. It may discuss an older listing, repeat an earlier report, or offer an interpretation without new evidence.
Look for a clear timeline, an identifiable source, and an explanation of how the claim was checked. If a page provides a dramatic victim count or claims to know exactly what the archive contains, ask whether it offers reliable evidence to support those details.
You should not need to download a suspicious archive to verify a report. In fact, doing so can introduce additional security and privacy risks.
Separate Facts From Speculation
Use careful language when summarizing uncertain reports. Terms such as “alleged,” “reported,” and “unverified” help distinguish a claim from an established finding.
Avoid statements that assign blame to a company or individual without evidence. Also avoid repeating claims about passwords, financial records, private images, or the number of victims unless credible sources confirm those details.
This approach is useful for readers and publishers alike. It supports accurate reporting, protects people from unnecessary alarm, and reduces the chance of turning an unsupported rumor into an apparent fact.
Legal and Ethical Concerns Around Leaked Material
The legal implications of accessing, downloading, or sharing leaked material depend on what the material contains, how it was obtained, what someone does with it, and which laws apply. It would be inaccurate to claim that every visit to a page discussing a leak is illegal. However, some activities can create significant legal risks.
For example, knowingly accessing or distributing stolen credentials, using another person’s account without authorization, or sharing copyrighted material without permission may violate applicable laws. Unauthorized disclosure of sensitive personal information can also raise privacy concerns.
U.S. readers should distinguish between reading a legitimate news report about a security incident and obtaining or redistributing the underlying material. The former can serve a valid public-interest purpose. The latter may harm victims or cross legal boundaries, depending on the circumstances.
There are ethical concerns as well. People whose information appears in an alleged leak may never have agreed to its publication. Sharing private files can spread the harm even when the person forwarding them did not create the original archive.
If you encounter sensitive material, do not republish it to prove that it exists. Preserve only the information needed to report the issue safely, follow the relevant platform’s reporting process, and seek qualified legal advice if you believe you may be directly affected.
What Should You Do If You Already Opened a Suspicious File?
Opening an unknown file does not automatically mean your device has been compromised. The appropriate response depends on what you opened, what happened afterward, and whether you installed anything or entered account information.
If you only visited a page and closed it, update your browser and operating system, review any unexpected downloads, and watch for unusual account activity. Do not assume that a compromise occurred solely because the page was associated with a leak.
If you downloaded or ran a suspicious file, take the situation more seriously. Disconnect the affected device from the internet if you suspect active malicious activity, and use trusted security software or professional support to assess it. Avoid entering passwords or accessing sensitive accounts from a device you believe may be compromised.
If you entered a password into a suspicious page, change it from a trusted device. Change the same password anywhere else you reused it, enable MFA, and review active sessions. If you provided payment information, contact your bank or card issuer through an official channel.
Keep records of suspicious messages, timestamps, and account alerts when needed for reporting. Do not forward the suspected malware or redistribute private files to others as evidence.
Frequently Asked Questions
1. What is thejavasea.me leaks aio-tlp371?
It is a search term associated with an alleged online archive or collection labeled AIO-TLP371. Its exact contents, origin, and authenticity have not been independently verified.
2. Is AIO-TLP371 a confirmed data breach?
Public information reviewed for this article does not establish AIO-TLP371 as a confirmed data breach with verified victims or a known source. Treat specific claims cautiously until credible evidence becomes available.
3. Is TheJavaSea.me safe to visit or download files from?
The safety of a website or file cannot be established by its name or online descriptions alone. Avoid downloading unknown archives, running unfamiliar files, or entering personal information on untrusted pages.
4. How can I check whether my information was exposed?
Use a reputable breach-notification service, review official security alerts, and check your accounts for unfamiliar activity. Have I Been Pwned can help you check whether your email address appears in known breaches.
5. What should I do if my password appears in a leak?
Change the affected password immediately and update it anywhere else you reused it. Enable multifactor authentication, review recent account activity, and contact the service provider if you notice unauthorized access.
Conclusion
The keyword thejavasea.me leaks aio-tlp371 refers to online discussions about an alleged leak-related archive, but its exact contents, origin, and scope remain unverified. It is important to distinguish repeated internet claims from independently confirmed cybersecurity findings. The label alone does not prove that a new data breach occurred or that your personal information was exposed.
The safest response is to avoid downloading unknown files, verify reports through credible sources, and strengthen your account security. Use unique passwords, enable multifactor authentication, and check for suspicious activity. If you discover signs of identity theft or unauthorized access, take action through official service providers and trusted reporting channels. Staying cautious helps protect your privacy without spreading unsupported claims.
Humair is the founder of PeakMagzine.com and a seasoned digital strategist with over 15 years of SEO experience. He specializes in creating high-quality, optimized content that drives organic traffic, improves search rankings, and helps brands grow their online presence effectively.
